5 Impacts of Cyberattacks on Business Operations and Continuity
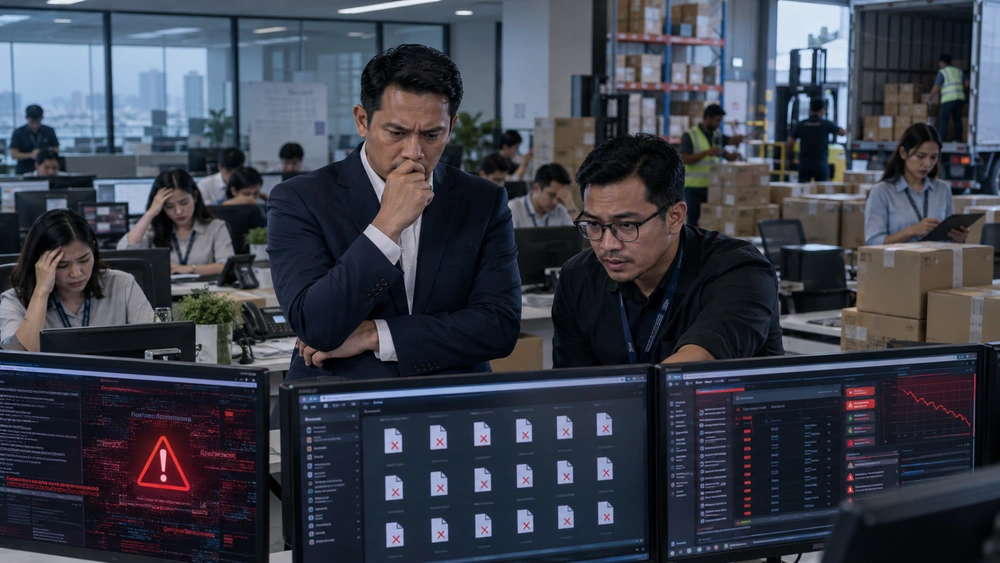
The five main impacts of cyberattacks on companies include:
- Disrupted business operations and services.
- Critical data becoming inaccessible or unusable.
- Higher recovery costs and disrupted revenue.
- Legal, contractual, and compliance risks.
- Declining customer and partner trust.
The severity of a cyberattack depends on the systems and data affected, the duration of the disruption, and the company’s recovery readiness. An attack on a single application can disrupt operations, transactions, customer service, and relationships with business partners.
According to Verizon’s 2026 Data Breach Investigations Report, ransomware was involved in 48% of the data breaches analyzed. This finding shows that ransomware is not merely a technical issue affecting devices. It is also a threat to business continuity.
Note: Incident handling, system recovery, and legal compliance must be based on investigation findings, the types of data involved, contractual obligations, the company’s industry, and applicable regulations. Systems should not be reactivated until their security and integrity have been assessed by qualified personnel.
Business Operations and Services Are Disrupted
Operational disruption caused by a cyberattack can simultaneously halt production, order processing, payments, deliveries, customer service, and internal coordination.
1. Critical Systems Become Inaccessible
Ransomware can lock applications and data, while account takeovers or network disruptions can prevent users from accessing critical systems. Affected systems may also need to be deliberately isolated to stop the attack from spreading.
2. Business Processes Come to an Immediate Halt
Processes that depend entirely on applications, databases, networks, or user accounts cannot continue. Manual alternatives may also be unavailable when all supporting information is stored within the affected system.
3. Production and Deliveries Are Delayed
Disruptions to inventory data, production schedules, warehouse systems, or logistics platforms can prevent teams from identifying available products, determining which orders to process, and confirming delivery destinations.
4. Customer Service Teams Cannot Operate Normally
Customer service teams will struggle to provide accurate answers when they cannot access transaction histories, service tickets, order statuses, or customer information.

Critical Data Becomes Inaccessible or Unusable
A corporate data breach is not the only risk. Data may also be locked, lost, damaged, or remain available while its reliability can no longer be guaranteed.
1. Data Is Locked by Ransomware
Ransomware can prevent a company from accessing files, databases, applications, and backups that remain connected to the affected systems.
2. Data Is Lost or Damaged
Deletion by attackers, system damage, or an incorrect recovery process can leave data incomplete and difficult to restore.
3. Data Is Exposed to Unauthorized Parties
Customer, employee, transaction, credential, and internal document data may be copied before the system is locked. Restoring system access does not automatically prove that no data breach occurred.
4. Data Integrity Cannot Be Confirmed
Changes to bank account details, inventory records, access rights, or transactions may not be immediately visible. Activity logs, change histories, and reliable comparison sources must be examined before the data is used again.
5. Decision-Making Is Delayed
Management cannot rely on dashboards, financial reports, or operational data until the source and validity of the information have been confirmed.
| Data Condition | Example of Impact | Affected Process | Required Check |
| Locked or lost | Data is unavailable | Operations and transactions | Backup availability and recoverability |
| Exposed | Information is controlled by unauthorized parties | Customer service and compliance | Access logs and scope of affected data |
| Suspected of being altered | Information cannot be trusted | Reporting and decision-making | Data integrity and change history |
Recovery Costs Increase and Revenue Is Disrupted
Losses from a cyberattack include direct incident-handling costs, reduced productivity, and delayed revenue while business operations remain unavailable.
1. Investigation and Incident-Handling Costs Increase
A company may require forensic analysis, cybersecurity specialists, data recovery, crisis communication, and additional monitoring to determine the scope of the attack.
2. Repairing or Replacing Systems Requires Additional Costs
Servers, software, configurations, credentials, devices, and parts of the infrastructure may need to be cleaned, reconfigured, replaced, or rebuilt.
3. Employee Productivity Declines
Employees lose working time when access is interrupted, they must assist with data reconciliation, or they have to use slower and more error-prone manual processes.
4. Transactions and Revenue Are Delayed
Sales, invoicing, payments, production, and deliveries may stop. Losses should be calculated based on the transactions and processes that were actually affected.
5. Recovery Can Take Longer Than the Technical Disruption
Even after systems are restored, the company may still need to process backlogs, reconcile transactions, repair data, and complete delayed services.
| Cost Category | Source of Cost | Data Needed to Calculate the Impact |
| Technical response | Specialists, devices, and software | Working hours and vendor costs |
| Productivity | Teams cannot work normally | Number of affected teams and disruption duration |
| Revenue | Delayed or canceled transactions | Transaction volume and margins |
| Extended recovery | Backlogs and reconciliation | Volume of outstanding work |
Cyberattack recovery costs cannot be determined using a single average figure. Each company must calculate the impact based on affected processes, disruption duration, transaction volume, and business obligations.
Companies Face Legal, Contractual, and Compliance Risks
Legal risks may arise when an incident involves personal data, customer services, critical systems, or specific obligations under contracts and industry regulations.
1. An Incident May Involve a Personal Data Protection Failure
If an attack involves personal data, the company must identify the types of data, data subjects, affected systems, and the possibility of unauthorized access or disclosure. Under Law Number 27 of 2022 on Personal Data Protection, personal data controllers are responsible for maintaining the security of personal data processing and responding to personal data protection failures.
2. Customer or Partner Contracts May Be Affected
Downtime, data loss, or failure to meet agreed service levels may trigger notification, remediation, compensation, or other contractual obligations.
3. The Company May Have Reporting Obligations
The parties that must be notified and the applicable reporting deadlines should be verified based on the type of incident, industry, affected data, contracts, and relevant regulations.
4. Incident Documentation Must Be Retained
Timelines, technical evidence, affected systems, decisions, recovery actions, and communications should be retained to support investigations and fulfill the company’s obligations.
5. Communication Errors Can Increase Risk
Rushed, inconsistent, or unverified information can create confusion among customers, partners, regulators, and internal teams.
Customer and Partner Trust Declines
Trust can decline when customers and partners question a company’s ability to protect data, maintain services, and respond effectively to security incidents.
1. Customers Question the Security of Their Data
Concerns will increase when an incident involves personal data, accounts, transactions, or confidential customer information.
2. Partners Reassess the Risks of the Relationship
Business partners may request audits, evidence of remediation, additional controls, or changes to contractual security requirements.
3. Sales Teams Face Greater Difficulty Convincing Prospects
A company’s incident history and cybersecurity readiness may become additional considerations when prospective customers evaluate it as a potential vendor.
4. Unclear Communication Worsens Public Perception
Remaining silent for too long, downplaying the impact, or changing statements without explanation can deepen distrust.
5. Rebuilding Trust Requires Evidence of Improvement
Trust must be rebuilt through corrective actions, stronger controls, improved monitoring, and follow-up measures that can be verified.
A Single Disruption Can Trigger a Chain Reaction
These five impacts do not occur independently. For example, ransomware can trigger the following chain of problems:
- Systems and data become inaccessible.
- Production, transactions, or deliveries stop.
- Revenue is delayed and recovery costs increase.
- Obligations to customers or partners are not fulfilled.
- Trust in the company declines.
Without prompt containment, a single technical disruption can develop into operational, financial, compliance, and reputational problems.

Measure the Potential Impact Before an Incident Occurs
Impact assessment helps companies prioritize protection based on the importance of business processes rather than focusing only on devices that appear critical.
1. Identify Systems and Data Supporting Critical Processes
Map the relationships between applications, databases, users, customers, vendors, and the business processes they support.
2. Determine the Impact if a System Becomes Unavailable
Assess the consequences for operations, transactions, customers, safety, contracts, and compliance.
3. Define the Maximum Tolerable Downtime
Determine how long each process can remain unavailable before the impact becomes critical to the business.
4. Review Backup and Recovery Readiness
Confirm that backups are available, isolated, protected, and regularly tested. A backup that cannot be successfully restored does not provide reliable recovery assurance.
5. Establish Protection and Recovery Priorities
Systems capable of disrupting transactions, customer service, or contractual commitments should receive a higher priority. Companies can assess their security controls and readiness through SMART IT’s Cyber Security services.
According to The NIST Cybersecurity Framework (CSF) 2.0, cybersecurity risk management consists of six interconnected functions: Govern, Identify, Protect, Detect, Respond, and Recover. This means companies should not rely solely on protective controls. They must also identify risks, detect incidents, prepare an effective response, and ensure that operations can be restored.
| System | Supported Process | Impact if Unavailable | Downtime Tolerance | Backup Status | Priority |
| Application name | Transactions or operations | Operational, financial, and compliance impacts | Measurable time limit | Backup location and test results | High, medium, or low |
FAQs About the Impact of Cyberattacks on Companies
The following answers address common questions about the business impact of cyberattacks and corporate recovery readiness.
1. Do Cyberattacks Always Cause Data Breaches?
No. Cyberattacks may disrupt system availability or alter data without evidence that information has been exposed.
2. Are Backups Enough to Reduce Every Impact of a Cyberattack?
No. Backups support data recovery, but companies also need protection, detection, incident response, communication, and operational recovery plans.
3. Why Can Ransomware Stop Business Operations?
Ransomware can lock the data and applications used for order processing, production, payments, deliveries, and other business processes.
4. What Is the Difference Between Ordinary Downtime and a Cyberattack-Related Disruption?
A cyberattack-related disruption requires an investigation and security and integrity checks before systems can be safely reactivated.
5. Can Small Businesses Also Experience Severe Impacts?
Yes. The severity depends on the company’s reliance on its systems, the processes affected, the disruption duration, and its recovery capabilities.
6. Which Impact of a Cyberattack Is the Most Difficult to Recover From?
Customer and partner trust often takes longer to restore because it cannot be recovered simply by bringing systems back online.
Conclusion
If the loss of a single system can disrupt transactions, customer service, production, or contractual commitments, that system should become a protection and recovery priority. Map critical systems, define downtime tolerances, test backups, and establish appropriate security controls and recovery procedures before an incident occurs.
Prevent Cyber Disruptions from Becoming Wider Business Losses
SMART IT can help companies assess their system security through Cyber Security services and a Web Application Firewall that protects web applications and APIs using solutions from Cloudflare and Cloudbric. Discuss your company’s security requirements with SMART IT to prevent cyber incidents from developing into operational shutdowns, data loss, and broader business losses.
PT SMARTIT MANTAP DIGITAL INDONESIA
Vieloft Ciputra World, Suite 10-01
Ciputra World Superblock Complex
Jl. Mayjen Sungkono No. 89
Surabaya, East Java, Indonesia 60224
Phone: +62 811 3057 6888 / +62 811 3426 391
Email: hello@smart-it.co.id
Facebook: Smart IT Indonesia
LinkedIn: Smart IT Indonesia
Instagram: smartitcoid
References
1. National Institute of Standards and Technology. (2024). The NIST Cybersecurity Framework (CSF) 2.0 (NIST CSWP 29). U.S. Department of Commerce.
https://doi.org/10.6028/NIST.CSWP.29
2. Government of the Republic of Indonesia. (2022). Law of the Republic of Indonesia Number 27 of 2022 on Personal Data Protection. JDIH BPK.
https://peraturan.bpk.go.id/Details/229798/uu-no-27-tahun-2022
3. Verizon. (2026). 2026 Data Breach Investigations Report. Verizon Business.
Related Articles
 Cyber Security
Why Isn’t Cybersecurity Solely the IT Team’s Responsibility?
 Cyber Security
Strengthen Your Business Digital Security Before It’s Too Late: Protect Your Website from DDoS Attacks and Data Breaches
 Cyber Security