Why Isn’t Cybersecurity Solely the IT Team’s Responsibility?
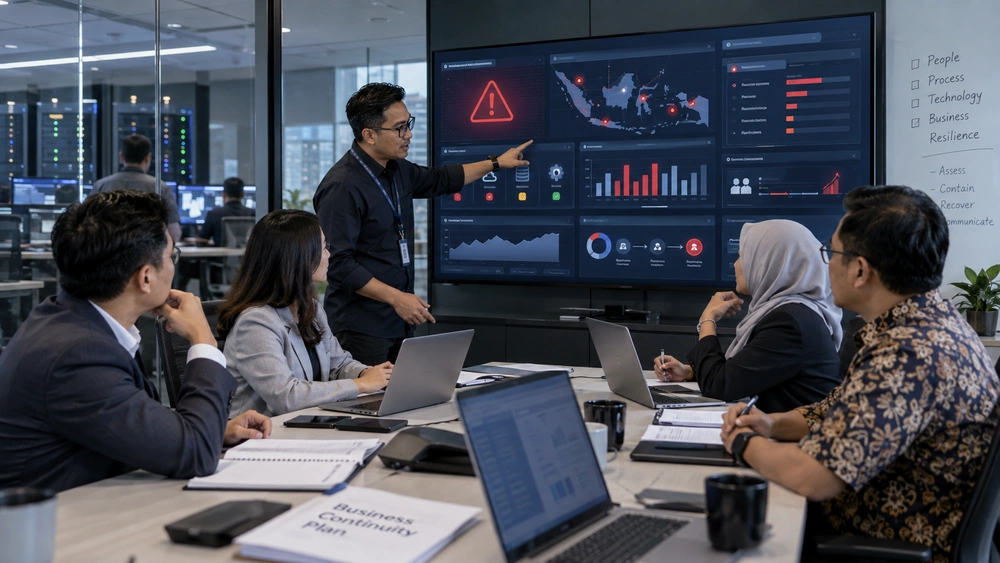
Cybersecurity for business is not solely the IT team’s responsibility because cyber risks can:
- Disrupt system-dependent operational processes.
- Delay transactions, revenue, and customer service.
- Create legal, contractual, and compliance obligations.
- Damage the company’s reputation and clients’ trust.
- Require risk, budget, communication, and recovery decisions beyond the IT team’s technical authority.
The IT team manages technical controls, while management determines priorities, risk tolerance, and incident preparedness. This division of responsibility is essential because system disruptions can directly affect operations, transactions, and customer service.
Under Article 57 of Law Number 27 of 2022 concerning Personal Data Protection, violations of certain obligations may result in administrative sanctions, ranging from written warnings to fines of up to 2% of annual revenue or annual income, depending on the relevant violation variables.
Note: This provision does not mean that every cyberattack automatically results in sanctions. Data protection, reporting, and communication obligations should be assessed with legal or compliance functions based on the type of data, business sector, contracts, and applicable regulations.
Digital Systems Have Become Part of Business Operations
Digital systems no longer support administrative work alone. They can drive production, transactions, communication, service delivery, and decision-making.
1. Critical Processes Depend on System Availability
Ordering, production, warehousing, shipping, payments, HR, and customer service may be disrupted when applications or networks become unavailable. The level of risk should be assessed according to the processes that depend on each system.
2. Disruption to One System Can Affect Multiple Processes
System integration means that disruption to user identities, databases, APIs, cloud services, or core applications may affect several departments simultaneously. Dependency mapping helps companies identify these potential cascading effects.
3. Manual Procedures May Not Be Able to Replace Digital Systems
Manual processes may be unable to handle transaction volumes, data requirements, authorizations, and synchronization across platforms. Companies should test alternative procedures instead of assuming that all work can simply be transferred to spreadsheets or physical documents.

Security Disruptions Can Delay Transactions and Services
The impact of a cyberattack should be measured by the transactions and services that cannot be completed, not only by the number of affected devices.
1. Transactions May Be Delayed or Unable to Be Processed
Disruptions to applications, databases, payment systems, accounts, or networks may interfere with sales, payments, and billing.
2. Teams May Be Unable to Serve Clients as Usual
Employees may lose access to order statuses, communication histories, or customer information, preventing them from providing clear service updates.
3. Service and Revenue Targets May Be Affected
The duration of a disruption should be translated into delayed transactions, backlogs, lost working hours, and unmet service targets.
The following table can help connect system disruptions with their business impact and tolerable downtime.
| Affected System | Business Process | Interrupted Transaction or Service | Affected Parties | Tolerance Limit |
| Sales application | Ordering | Orders cannot be processed | Customers and sales team | Determined by the process owner |
| Payment system | Payment processing | Transactions are delayed or fail | Customers and finance team | Based on transaction requirements |
| Customer database | Customer service | Customer information cannot be accessed | Customer service team and customers | Based on service targets |
| Warehouse system | Order fulfilment | Inventory and shipments are difficult to verify | Warehouse, sales team, and customers | Based on the operational schedule |
Cyber Risks Can Create Corporate Obligations
An incident may involve personal data, customer contracts, vendor requirements, service standards, and sector-specific regulations.
1. Incidents May Involve Customer and Employee Data
Management should understand the types of data being processed, where the data is stored, who has access, and the potential impact if the data is exposed, lost, or altered.
2. Companies May Have Contractual Obligations
System disruptions or data loss may affect compliance with service-level agreements, confidentiality provisions, support commitments, and other terms agreed upon with clients or vendors.
3. Reporting Decisions Cannot Be Made by the IT Team Alone
The technical team provides verified facts about an incident. However, legal, compliance, and management functions must assess reporting and communication obligations based on the data involved, contractual terms, business sector, and applicable regulations.
Client Trust Is Part of Cyber Risk
Customers and partners assess not only service quality but also the company’s ability to protect data and maintain operations.
1. Clients May Question the Company’s Ability to Protect Data
Concerns may increase when an incident involves confidential information, accounts, transactions, or personal data.
2. Partners May Reassess the Business Relationship
An incident may lead to additional audits, revised security requirements, requests for evidence of remediation, or a reassessment of the company as a vendor.
3. Reputational Damage Does Not End When Systems Are Restored
Systems may be restored faster than trust. Delayed or inconsistent communication can also prolong reputational damage.
4. Restoring Trust Requires Evidence
Companies should demonstrate improvements in controls, monitoring, governance, and response preparedness. Simply stating that the system is secure may not be enough to address clients’ concerns.
Critical Incident Decisions Are Beyond the IT Team’s Authority
Technical teams can provide analysis and recommendations. However, decisions with operational, legal, financial, and reputational consequences require cross-functional approval.
1. Deciding Whether a System Should Be Shut Down
Isolation can contain an attack, but it may also stop critical processes. The decision should consider both the risk of further spread and the impact of service interruption.
2. Deciding Which Services Should Be Restored First
Recovery priorities should reflect process criticality, system dependencies, customer needs, and downtime tolerance.
3. Approving Communications to Relevant Parties
Information shared with employees, customers, partners, regulators, or the public should be based on verified facts and approved by the relevant functions.
4. Accepting the Risk of Reactivating a System
Reactivation should consider investigation findings, the risk of repeat attacks, operational requirements, and the temporary controls available.

Management Must Establish Risk Tolerance and Protection Priorities
Management should determine business requirements and acceptable risk limits before the IT team selects the technologies and security controls to implement.
1. Identify the Most Critical Business Services
Determine which processes cannot remain unavailable for long, as well as the customers and obligations that depend on those processes.
2. Define Unacceptable Impacts
These may include the loss of certain data, transaction stoppages, unauthorized data changes, or service disruptions that exceed the company’s tolerance limits.
3. Prioritize Budgets Based on Business Impact
Systems with the most serious consequences should receive stronger protection, monitoring, backup, and recovery capabilities.
4. Determine Which Risks Can Be Accepted or Must Be Reduced
Not every risk can be eliminated. Management must decide whether each risk should be avoided, reduced, transferred, or accepted for documented reasons.
The following matrix helps management connect cyber risks with their potential impact and appropriate treatment decisions.
| Cyber Risk | Related System | Operational Impact | Impact on Customers | Likelihood | Decision |
| Ransomware | Applications and databases | Operations stop | Services become unavailable | Assessed according to system conditions | Reduce |
| Data breach | Customer database | Investigation and access restrictions | Data may be exposed | Assessed according to existing controls | Reduce or transfer |
| Cloud vendor disruption | Cloud-based services | Applications cannot be used | Services are delayed | Assessed using service history and SLA | Reduce or accept |
| Administrator account takeover | Core systems | Unauthorized changes | Services and data are at risk | Assessed according to access controls | Avoid or reduce |
Cybersecurity Requires Cross-Functional Responsibility
Cross-functional involvement does not mean that every employee must handle technical work. Each party should fulfil responsibilities that match its authority and expertise.
| Function | Primary Responsibility | Decision or Contribution |
| Board of directors | Establish direction and oversight | Priorities, risk tolerance, and resources |
| Process owners | Identify critical systems and data | Business impact and disruption tolerance |
| IT or security | Operate technical controls | Access, patching, monitoring, detection, response, and recovery |
| Legal and compliance | Review obligations | Regulations, contracts, documentation, reporting, and communication |
| HR and employees | Maintain security in daily activities | Training, access management, procedural compliance, and reporting |
| Procurement | Manage vendor risk | Access requirements, security, incident notification, and service termination |
1. The Board Establishes Direction and Oversight
The board ensures that cyber risk is monitored as part of enterprise risk and that resources are allocated according to business priorities.
2. Process Owners Identify Critical Systems and Data
Business departments explain the impact if a process, application, or dataset becomes unavailable, exposed, or altered.
3. The IT or Security Team Operates Technical Controls
The IT team implements protection, access controls, patching, monitoring, detection, response, and technical recovery. These measures should be supported by fundamental corporate cybersecurity practices that also involve users.
4. Legal and Compliance Review Corporate Obligations
These functions assess regulations, contracts, documentation, reporting obligations, and incident communications.
5. HR and All Employees Maintain Security in Daily Activities
HR supports security training and access management throughout the employee lifecycle. Every user should also follow established procedures and report suspicious activities.
6. Procurement Manages Vendor Risk
Procurement should ensure that access requirements, data security, incident notifications, support arrangements, and service termination are addressed in vendor agreements.
Use Business Language in Cyber Risk Reports
Cyber risk reports should translate technical findings into information that helps management establish priorities and make decisions.
1. Do Not Stop at the Number of Alerts and Attacks
The number of blocked threats does not explain which services, transactions, or customers are at risk.
2. Connect Vulnerabilities with Assets and Business Processes
Identify the affected system, the business functions that depend on it, and the consequences if the vulnerability is exploited.
3. Show Remediation Progress and Residual Risk
Explain the actions already completed, existing obstacles, completion targets, risk owners, and outstanding decisions.
4. Report Response and Recovery Readiness
Include the results of backup tests, incident simulations, recovery times, and any coordination gaps identified.
Test Preparedness Through Cross-Functional Incident Simulations
Simulations help companies test roles and decision-making authority before a real incident occurs.
1. Use Scenarios That Disrupt Critical Processes
Select scenarios such as ransomware, a data breach, an administrator account takeover, or an unavailable cloud service.
2. Test Escalation Paths and Decision-Making Authority
Confirm who receives the initial report, declares an incident, approves a system shutdown, and establishes recovery priorities.
3. Test Communications with Employees and Clients
Ensure that messages use verified information, have an authorized approver, and can be delivered through alternative channels if the primary system is unavailable.
4. Document Gaps That Must Be Addressed
The simulation should result in improvements to procedures, contact lists, controls, backups, documentation, and assigned responsibilities.
The NIST Cybersecurity Framework 2.0 places Govern alongside Identify, Protect, Detect, Respond, and Recover. This structure demonstrates that cyber risk management covers strategy, policies, roles, oversight, protection, response, and recovery, all of which should be managed in a coordinated manner.
FAQ
The following answers explain how cybersecurity responsibilities and governance should be distributed across a company.
1. Does Responsibility for Cybersecurity Still Rest with the IT Team?
The IT team is responsible for many technical controls. However, decisions involving risk and business impact require the participation of management and the relevant process owners.
2. Does the Board Need to Understand the Technical Details of Cybersecurity?
Not at an operational level. The board needs to understand risks, potential impacts, priorities, and the decisions that require its approval.
3. Who Owns Cyber Risk Within a Company?
Cyber risk ownership depends on the company’s structure and the affected processes. Responsibilities should be explicitly assigned to prevent unclear or conflicting accountability.
4. Is Purchasing Security Tools Enough?
No. Security tools must be supported by governance, processes, expertise, monitoring, response procedures, and recovery capabilities.
5. Why Should Business Process Owners Be Involved?
Process owners understand operational impacts, critical data, disruption tolerances, and the services that should be prioritized.
6. How Should Cyber Risk Be Reported to Management?
Connect technical risks with assets, business processes, customers, potential losses, existing controls, residual risks, and the decisions required.
Conclusion
If a system disruption can stop transactions, expose critical data, or affect customer service, cybersecurity should be managed as a business risk. Management must establish critical processes, disruption tolerances, budget priorities, and incident decision-making authority, while the IT team implements and tests the appropriate technical controls.
The next step is to map systems to business processes, assign clear responsibilities, and test the company’s preparedness through cross-functional incident simulations.
Manage Cyber Risks Before They Disrupt Your Business
If system security has become a concern for management, operational continuity, or client trust, SMART IT can help your company evaluate its cyber risks and protection requirements. Discuss your systems, critical processes, and priority risks to ensure that your company’s cybersecurity strategy aligns with its business needs.
PT SMARTIT MANTAP DIGITAL INDONESIA
Vieloft Ciputra World, Suite 10-01
Ciputra World Superblock Complex
Jl. Mayjen Sungkono No. 89, Surabaya, East Java, Indonesia 60224
Phone: +6281130576888 / +628113426391
Email: hello@smart-it.co.id
Facebook: Smart IT Indonesia
LinkedIn: Smart IT Indonesia
Instagram: smartitcoid
References
1. National Institute of Standards and Technology. (2024). The NIST Cybersecurity Framework (CSF) 2.0 (NIST CSWP 29). U.S. Department of Commerce.
https://nvlpubs.nist.gov/nistpubs/CSWP/NIST.CSWP.29.pdf
2. Republic of Indonesia. (2022). Law of the Republic of Indonesia Number 27 of 2022 concerning Personal Data Protection. Legal Documentation and Information Network of the Ministry of Communication and Digital Affairs.
https://jdih.komdigi.go.id/produk_hukum/view/id/832/t/undangundang%2Bnomor%2B27%2Btahun%2B2022
Related Articles
 Cyber Security
5 Impacts of Cyberattacks on Business Operations and Continuity
 Cyber Security
Strengthen Your Business Digital Security Before It’s Too Late: Protect Your Website from DDoS Attacks and Data Breaches
 Cyber Security